Unpatchable OT: IEC 62443 zones and conduits for NIS2
Compensating controls for PLCs and SCADA and how to scope the plant network for NIS2 reporting
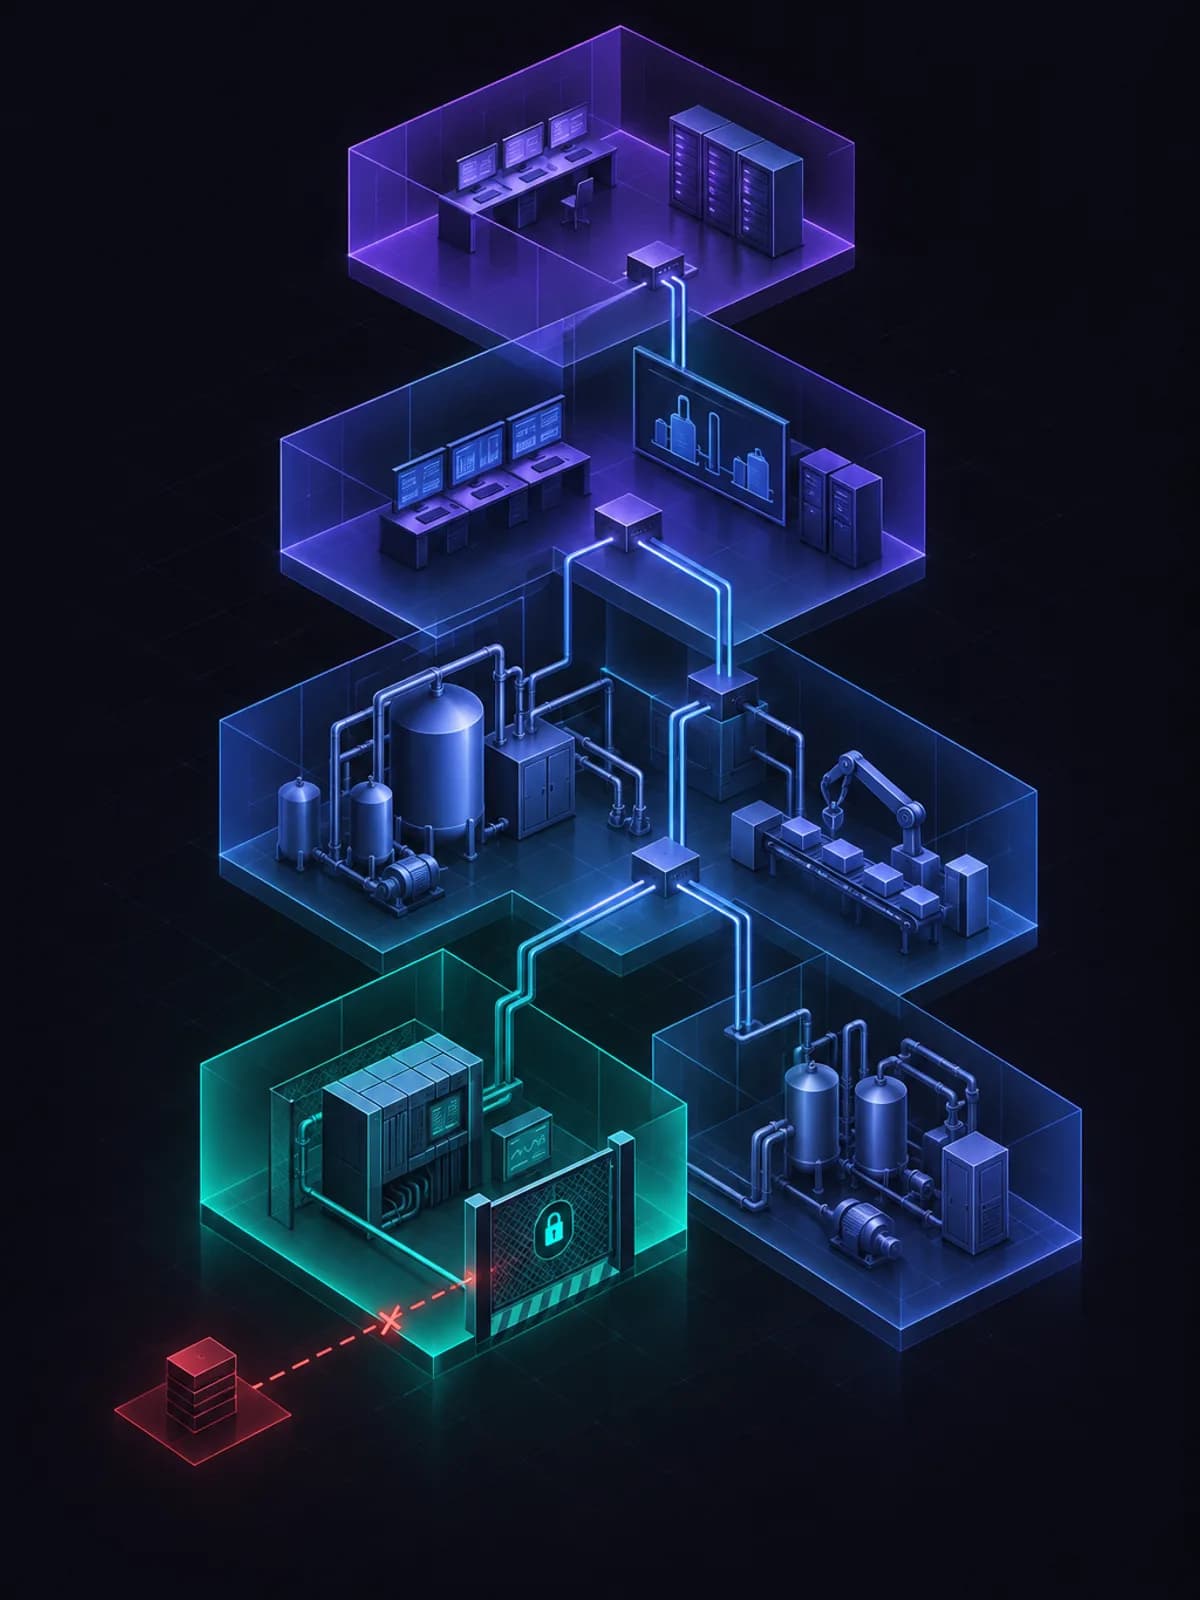
Industria/OT-NIS2
Unpatchable OT: IEC 62443 zones and conduits for NIS2
A practical guide to protect PLCs and SCADA systems that cannot be patched and to scope IEC 62443 zones and conduits so the plant network also serves NIS2 reporting. It starts from the attacks on European supermarket refrigeration controllers (October and November 2026) and includes nine compensating controls, a zones and conduits method, the mapping to NIS2 measures and deadlines, a phased plan and a checklist.
Contents / Contenido
- Executive summaryPreview
- 1. The case: when the controller cannot be patchedPreview
- 2. Why OT does not get patchedRequires download
- 3. Nine controls to protect PLCs and SCADA that cannot be patchedRequires download
- 4. IEC 62443 zones and conduits, step by stepRequires download
- 5. Making the plant network also satisfy NIS2 reportingRequires download
- 6. Phased planRequires download
- 7. ChecklistRequires download
- 8. Where HodeiShield fitsRequires download
- SourcesRequires download
Preview: first pages
A practical guide to protect PLCs and SCADA systems that cannot be patched and to scope IEC 62443 zones and conduits so the plant network also serves NIS2 reporting. It starts from the attacks on European supermarket refrigeration controllers (October and November 2026) and includes nine compensating controls, a zones and conduits method, the mapping to NIS2 measures and deadlines, a phased plan and a checklist.
The preview of this whitepaper includes the executive summary, regulatory context and methodological approach that frames the rest of the document. Download to access full templates, matrices and checklists.
- Executive summary
- 1. The case: when the controller cannot be patched
Sources
- CERTFR-2026-ALE-012: Security incident targeting remote controllers of refrigeration installations — CERT-FR (ANSSI), 2026-10-12
- Cyberattack on fridges hits supermarkets across Europe — CNBC (Reuters), 2026-11-02
- Cyberattack shuts down refrigerators at French supermarkets — BleepingComputer, 2026-10-12
- Guide to Operational Technology (OT) Security (SP 800-82 Rev. 3) — NIST, 2023-09-28
- Primary Mitigations to Reduce Cyber Threats to Operational Technology — CISA, 2025-05-06
- IEC 62443-3-2:2020 Security for industrial automation and control systems, Part 3-2: Security risk assessment for system design — IEC, 2020-06-24
- IEC 62443-3-3 Industrial communication networks, Network and system security, Part 3-3: System security requirements and security levels — IEC, 2013-08-07
- ISA/IEC 62443 series of standards — ISA
- Directive (EU) 2022/2555 on measures for a high common level of cybersecurity across the Union (NIS2) — EUR-Lex (Official Journal of the EU), 2022-12-14
- Commission refers Ireland, Spain, France and the Netherlands to the Court of Justice for failing to transpose the rules on cybersecurity — European Commission, 2026-07-08
- Hackers disrupt refrigeration systems at European supermarkets — BleepingComputer, 2026-11-02
- Proyectos de ley de la legislatura actual (datos abiertos, descarga del 3 de noviembre de 2026) — Congreso de los Diputados, 2026-11-03
- Real Decreto 806/2026, de 5 de octubre, de disolución del Congreso de los Diputados y del Senado y de convocatoria de elecciones — Boletín Oficial del Estado, 2026-10-06
Frequently asked questions
- How do I protect PLCs and SCADA systems that cannot be patched?
- With compensating controls: remove Internet exposure, secure remote access with multi-factor authentication, segment into zones, harden credentials and configuration, monitor traffic, keep configuration backups and rehearse manual operation. Record each patching exception with an owner and a review date.
- How are IEC 62443 zones and conduits defined?
- You define the system under consideration, assess risk, group assets into zones by consequence of failure, technology and owner, identify the conduits between zones, assign a target security level and document the controls of each conduit.
- Is complying with IEC 62443 the same as complying with NIS2?
- No. NIS2 does not designate IEC 62443 as a route to compliance. But the zone and conduit register and the risk assessments produce evidence that is useful for several Article 21 measures and for the Article 23 incident reports.
- What deadlines does NIS2 set to report an incident?
- An early warning within 24 hours, an incident notification within 72 hours, an intermediate report on request and a final report no later than one month after the notification.

Gorka Gonzalo
Founder & CEO
Founded Hodeitek in 2023 and runs the company, after more than 8 years in pentesting, Red Team, OT/ICS auditing, and SOC leadership. A cybersecurity and AI expert, he sets the technical and product direction of HodeiShield and personally leads the most critical engagements — from defense strategy to applying AI in threat detection. He is the client's direct point of contact: whoever scopes the work also answers for the result.