Why is AI payment security important for building trust?
What changes when an agent pays for a person, the three guarantees merchants and users need, and what AP2, Visa, Mastercard and the PCI SSC say.

On this page
AI payment security matters because, when an AI agent pays for a person, the merchant, the bank and the user need proof of three things: that the agent is legitimate, that the person authorised this purchase within these limits, and that a record exists to resolve disputes. Without that proof, nobody trusts it.
What changes when an agent pays
Payment and anti-fraud systems were designed around one assumption: behind the purchase there is a person browsing. An agent breaks that assumption in two ways. First, it generates automated traffic that a merchant may confuse with malicious bots. Second, it sometimes acts without the person being present at the moment of payment.
Cloudflare explains the underlying problem: user agent and IP address fields can be spoofed, which leads to inaccurate classification of automated traffic [1]. That is why the new protocols rely on cryptographic signatures rather than on signals that are easy to imitate.
The three guarantees that sustain trust
1. Agent identity: who is asking to be paid?
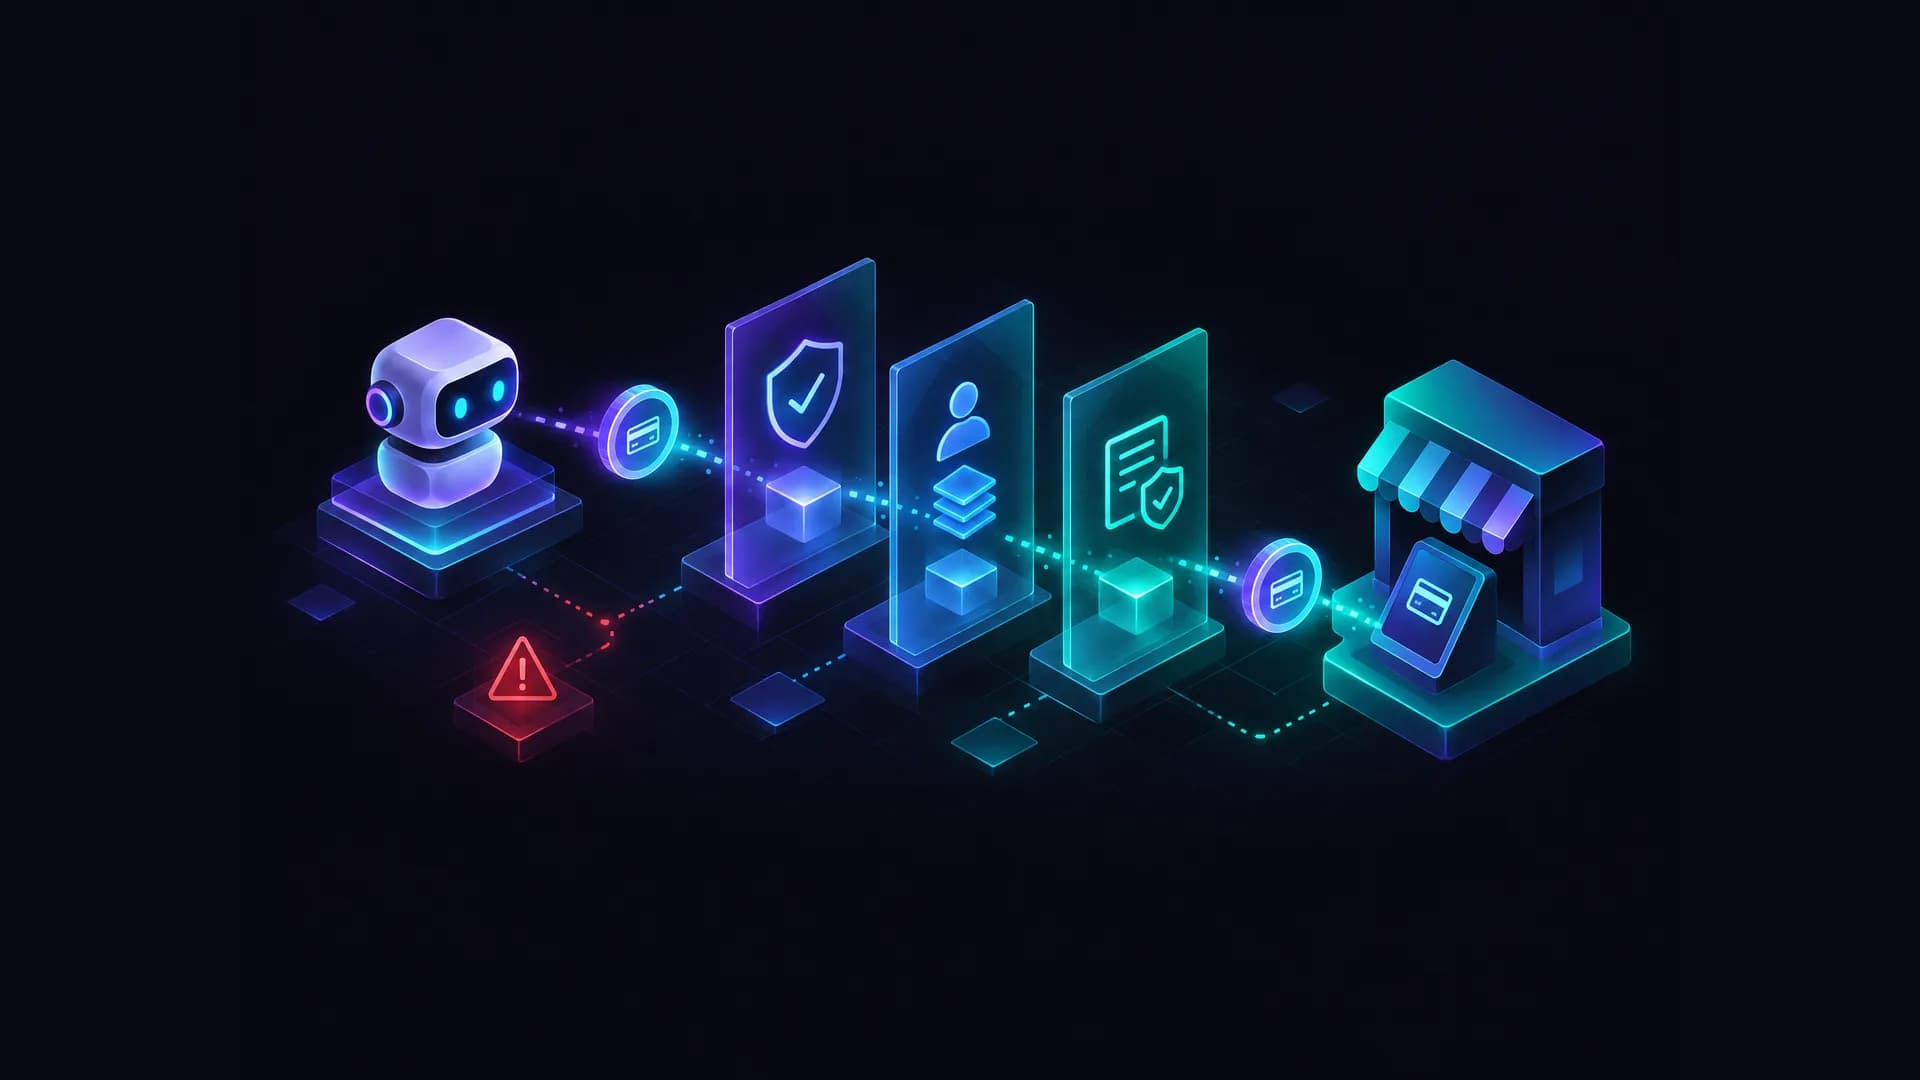
Visa describes its Trusted Agent Protocol as a verifiable, cryptographic standard to help merchants differentiate legitimate agents from malicious bots or crawlers [2]. According to Cloudflare's explanation, agents register and publish their public keys in a well-known directory; the merchant checks the signature on each request, which includes a nonce to prevent replay, and each protocol distinguishes whether the agent is only browsing or is about to pay [1].
2. User authorisation: who approved this purchase, within which limits?
The Agent Payments Protocol (AP2) proposes "mandates": cryptographically signed digital objects that capture what the person authorises. There is a checkout mandate shared with the merchant and a payment mandate shared with the credential provider, the networks and the processor; each has an open stage, with constraints such as budget or allowed instruments, and a closed stage that authorises a specific amount tied to a finalised checkout [3].
3. Traceability: what exactly happened if there is a dispute?
AP2 states that it provides a non-repudiable, cryptographic audit trail for every transaction, useful for resolving disputes [3]. Without a verifiable record, the argument between customer, merchant and issuer comes down to who has the more convincing version.
An illustrative case: a delegated purchase that gets disputed
An illustrative scenario, not a real case. A company delegates the purchase of office supplies to an agent with an open mandate: a maximum budget and a list of permitted merchants. The agent completes a purchase and the person in charge disputes it on seeing the charge.
With the three guarantees, the discussion is settled with evidence rather than versions. The request signature shows which agent asked to be paid; the signed mandate shows the limits the company set; the audit record shows whether the purchase respected them. If the agent exceeded them, there is a basis for a claim; if not, the company sees that the rule was poorly defined.
Without those records, customer, merchant and issuer only have competing versions. Who is responsible in each case still depends on the contract and the payment network rules.
What can go wrong: risks and controls
| Risk | What happens | Typical control |
|---|---|---|
| Spoofed agent | A bot pretends to be a trusted agent | Verifiable signature and a directory of registered agents [1] |
| Manipulated instructions | Malicious content in a page or email steers the agent into an unwanted purchase | Prompt injection testing and action limits; OWASP lists prompt injection and excessive agency among the risks of LLM applications [4] |
| Spend outside intent | The agent buys more, or elsewhere, than the person wanted | Mandates with bounded budget and instruments [3] |
| Request replay | An attacker resubmits a legitimate request | Signatures with a nonce and time validity [1] |
| Dispute without proof | Nobody can show what was authorised | Mandate chain and audit log [3] |
| Exposed payment data | Credentials or cardholder data pass through AI systems without control | Apply existing payment standards to AI systems [5] |
What payment bodies and standards say
- The PCI Security Standards Council published additional guidance on securing AI in payment environments on 7 October 2026. The guidance is not mandatory and, where it differs from an official PCI standard, the standard prevails. The announcement raises concern about AI systems that can act with limited human involvement and stresses that "clear accountability is what allows confidence in the system to hold" [5].
- AP2 is an open protocol under the Apache 2.0 licence; its standardisation continues in the FIDO Alliance working groups on agentic authentication and payments [3].
- Visa's and Mastercard's protocols build on the same agent-traffic authentication mechanism based on HTTP message signatures [1].
These frameworks are recent and still evolving: check the current version before designing on top of them.
What merchants and platforms should do
- Verify the agent's identity before accepting a payment from it, not only before letting it browse.
- Separate browsing from paying: different permissions and a different level of checks.
- Require authorisation with limits (amount, merchant, expiry) and record it.
- Keep evidence of every decision to handle disputes.
- Test the flow as an attacker would: spoofing, prompt injection in the content the agent reads, and abuse of purchase logic.
- Apply existing payment standards to the AI components that touch cardholder data [5].
What companies and people who delegate to an agent should do
- Set a maximum budget and a list of permitted merchants or categories.
- Require human approval for large amounts or irreversible purchases.
- Review transactions as often as you would a corporate card.
- Choose agents whose provider explains how each purchase is recorded and audited.
How we help
We assess AI flows from an attacker's perspective and help govern them: AI security consulting, pentesting and Red Team on applications and APIs, and the AI governance and security solution. If you need to build tools or agents with security controls by design, there is our software and AI for cybersecurity service. And to understand how an environment with agents is monitored, read what an agentic SOC is.
Frequently asked questions
What is an agentic payment?
A payment initiated and executed by an AI agent following the instructions and limits of a person or company, with or without their presence at the time of purchase.
What is a mandate in AP2?
A cryptographically signed digital object that records what the user authorises: the prior constraints (for example, a budget) and, in the closed stage, the authorisation of a specific purchase [3].
How does a merchant know an agent is legitimate?
By verifying the signature on its requests against the public keys the agent has registered in a directory, as the Visa and Mastercard protocols work according to Cloudflare [1].
Why is AI payment security important for building trust?
Because trust in a delegated payment depends on being able to show who authorised what, and within which limits. If the agent buys something unwanted, there is no universal answer on who is responsible: it depends on the contract, the payment network rules and the agent's provider. What can be said is that without verifiable authorisation and records it is almost impossible to determine; hence the PCI SSC's emphasis on clear accountability [5].
Is the PCI SSC guidance on AI mandatory?
No. The announcement itself says the additional guidance should not be considered mandatory requirements and that the official standard prevails in case of a difference [5].
Next step
Are you designing or assessing payments with AI agents? Let's talk before go-live. Payment and agent providers are part of your supply chain: HodeiShield helps manage third-party risk and compliance.
Sources
- Securing agentic commerce: helping AI Agents transact with Visa and Mastercard. Cloudflare, 2025-10-24. https://blog.cloudflare.com/secure-agentic-commerce/
- Trusted Agent Protocol. Visa Developer. https://developer.visa.com/capabilities/trusted-agent-protocol/overview
- Agent Payments Protocol (AP2). AP2 project. https://ap2-protocol.org/
- OWASP Top 10 for LLM Applications. OWASP GenAI Security Project. https://genai.owasp.org/llm-top-10/
- PCI SSC Publishes Additional Guidance on Securing AI in Payment Environments. PCI Security Standards Council, 2026-10-07. https://www.pcisecuritystandards.org/about_us/press_releases/pci-ssc-publishes-additional-guidance-on-securing-ai-in-payment-environments/
Was this article useful?
Gorka Gonzalo
Founder & CEO
Founded Hodeitek in 2023 and runs the company, after more than 8 years in pentesting, Red Team, OT/ICS auditing, and SOC leadership. A cybersecurity and AI expert, he sets the technical and product direction of HodeiShield and personally leads the most critical engagements — from defense strategy to applying AI in threat detection. He is the client's direct point of contact: whoever scopes the work also answers for the result.